As organizations manage employees across offices, homes, and multiple countries, controlling who can access company systems becomes more complex.
User management covers the processes and technologies used to create and manage user identities, authenticate users, assign access, update permissions, and remove access when it is no longer needed. It connects identity, access, security, and the employee lifecycle.
Modern user management should follow users as they join, change roles, and leave the organization. Microsoft, for example, describes identity lifecycle management around the joiner, mover, and leaver stages, with access changing as the user’s relationship with the organization changes.
For distributed businesses, this helps IT teams maintain consistent access without manually managing every account, application, and permission.
Is user management important?
Effective user management matters because access changes throughout the employee lifecycle. New hires need the right systems quickly, employees may need different permissions when their roles change, and departing users should lose access at the right time.
For founders and IT leaders managing hybrid or remote teams, user management supports several areas:
- Security: User management helps control who can access applications, data, and other company resources. Authentication, access policies, and least-privilege permissions reduce unnecessary exposure. Multi-factor authentication remains an important security control, while newer guidance also emphasizes phishing-resistant authentication methods such as WebAuthn and FIDO2 where stronger assurance is needed.
- Efficiency: Automated provisioning and deprovisioning can reduce repetitive account administration. New employees can receive appropriate access when they join, while permissions can be updated when roles change and removed when employees leave. Modern identity platforms can automate these joiner, mover, and leaver workflows.
- Compliance: Centralized identity and access controls can support compliance by creating clearer access records, enforcing consistent permissions, and helping organizations control how personal and sensitive data is accessed. Under the GDPR, individuals have rights including access, rectification, restriction, and erasure of personal data in applicable circumstances. User management can support these processes, but it does not guarantee GDPR compliance on its own.
- User experience: Employees need secure access without unnecessary friction. Features such as single sign-on, self-service password management, and automated account provisioning can reduce repetitive sign-ins and support requests while maintaining centralized control.
By understanding and leveraging these principles and strategies, organizations can ensure that your IT support infrastructure can become a strategic asset that drives your business’s growth and innovation.
The 4 core pillars of modern user management
Modern user management transcends traditional boundaries, adapting to the complexities of global, distributed, and highly mobile workforces. Central to this evolution are 4 principles that ensure security, efficiency, and scalability.

Centralized control and visibility
At the heart of effective user management is centralized control, enabling the control of user identities, access permissions, and security policies from a single point.
Centralized visibility becomes more important as application environments grow. Okta reported that the average number of apps used by its customers reached 101 in 2025, increasing the number of accounts and access points IT teams need to manage.
This unified approach not only simplifies administrative tasks but also enhances security by providing a clear, comprehensive view of all users across the organization.
Scalability and flexibility
As businesses grow and evolve, their user management systems must adapt to changing needs. Scalability ensures that the system can handle increasing users and more complex organizational structures without degradation in performance or user experience.
- Dynamic user groups: Modern user management systems allow for creating dynamic user groups based on attributes such as department, role, or location. This flexibility supports more granular and relevant access controls.
- Automated provisioning and de-provisioning: Automating the processes of adding new users and removing those who leave the organization or change roles ensures that access rights are always up-to-date, minimizing security risks.
Robust security measures
Security is a cornerstone of user management, with multiple layers of protection being essential to safeguard sensitive information and maintain regulatory compliance.
- Multi-Factor Authentication (MFA): MFA provides stronger protection than passwords alone, but not all methods are equally resistant to phishing. NIST recommends phishing-resistant authentication over manually entered one-time codes. Microsoft reported that more than 97% of identity attacks involved password spray or brute force, while modern MFA reduced compromise risk by over 99%.
- Single Sign-On (SSO): SSO allows employees to access multiple connected applications through a central identity provider. This can reduce password fatigue while giving IT teams greater control over authentication and access policies.
For higher-risk environments, organizations can combine these controls with passwordless authentication, device signals, Conditional Access, and other risk-based policies.
User-centric design
User management systems must not only be powerful and secure but also user-friendly, ensuring that employees can access the tools and information they need without unnecessary friction.
- Self-service capabilities: Allowing users to perform certain tasks, such as resetting passwords or updating personal information, reduces the administrative burden on IT teams and empowers users.
- Intuitive interfaces: User-friendly interfaces and clear navigation enhance the user experience, encouraging adoption and compliance with IT policies.
The goal is not to remove security controls but to make secure behavior easier for employees to follow.
5 advanced user management strategies
Organizations with distributed teams or complex SaaS environments can build on these foundations with more granular access strategies.
Role-based access control (RBAC)
RBAC is a foundational strategy in advanced user management, where access rights are assigned based on the roles within an organization rather than on individual user identities. This approach simplifies permissions administration, making it easier to manage users’ access to specific resources based on their job functions.
- Efficient permission allocation – RBAC reduces the complexity and potential errors associated with individual permission management by grouping permissions into roles.
- Enhanced security posture – Limiting access to resources based on roles minimizes the risk of unauthorized access, adhering to the principle of least privilege.
Attribute-based access control (ABAC)
Building on the concept of RBAC, ABAC provides even finer-grained control by considering multiple attributes, including user, resource, and environmental conditions. This dynamic approach allows for more nuanced and context-sensitive access decisions.
- Contextual access decisions – ABAC can evaluate multiple factors, such as location, time of day, and device security status, to make real-time access decisions.
- Adaptive security policies – The flexibility of ABAC supports the creation of policies that adapt to changing business needs and threat landscapes.
Just-in-time provisioning
Just-In-Time (JIT) provisioning represents a shift towards more agile and responsive user management. Instead of pre-provisioning accounts for all potential users, JIT provisioning creates user accounts and grants access on an as-needed basis at the moment of access.
- Reduced attack surface – By minimizing the number of permanently provisioned accounts, JIT provisioning reduces the potential attack surface for cyber threats.
- Operational efficiency – Automating the provisioning process based on real-time access requirements streamlines operations and enhances user experience.
Leveraging user management systems
To implement these advanced strategies effectively, leveraging comprehensive user management systems is crucial. These systems provide the tools and frameworks necessary to automate and enforce complex access policies.
- Centralized user management – A unified platform for managing user identities, access rights, and security policies ensures consistency and control across the organization.
- Integration with existing infrastructure – Effective user management systems seamlessly integrate with existing IT infrastructure, such as Active Directory and other central directory services, to leverage and enhance current capabilities.
Behavioral analytics and adaptive authentication
Modern access systems can also use risk signals to determine whether an authentication attempt requires additional verification.
These signals can include unusual sign-in patterns, leaked credentials, device status, user risk, location, or other contextual information.
- Risk detection: Identity platforms can identify unusual activity that may indicate a compromised account rather than relying only on static login rules.
- Context-sensitive authentication: Higher-risk events can trigger additional verification, remediation, or blocked access, while lower-risk activity can follow the normal authentication flow.
For example, Microsoft Entra ID Protection can calculate user risk and use Conditional Access policies to require remediation, password changes, or block access when risk conditions are met.
The purpose of adaptive authentication is not to continuously profile employees. It is to use relevant security signals to apply stronger controls when the access attempt presents greater risk.
Streamlining IT with advanced user management
User management connects onboarding, access control, role changes, and offboarding. Strategies such as RBAC, automated provisioning, and adaptive authentication help IT teams give employees the right access while reducing unnecessary permissions.
The wider employee IT lifecycle benefits from the same approach. Bunker, for example, achieved 2x faster device provisioning after introducing pre-configured laptops and centralized device management through Esevel.
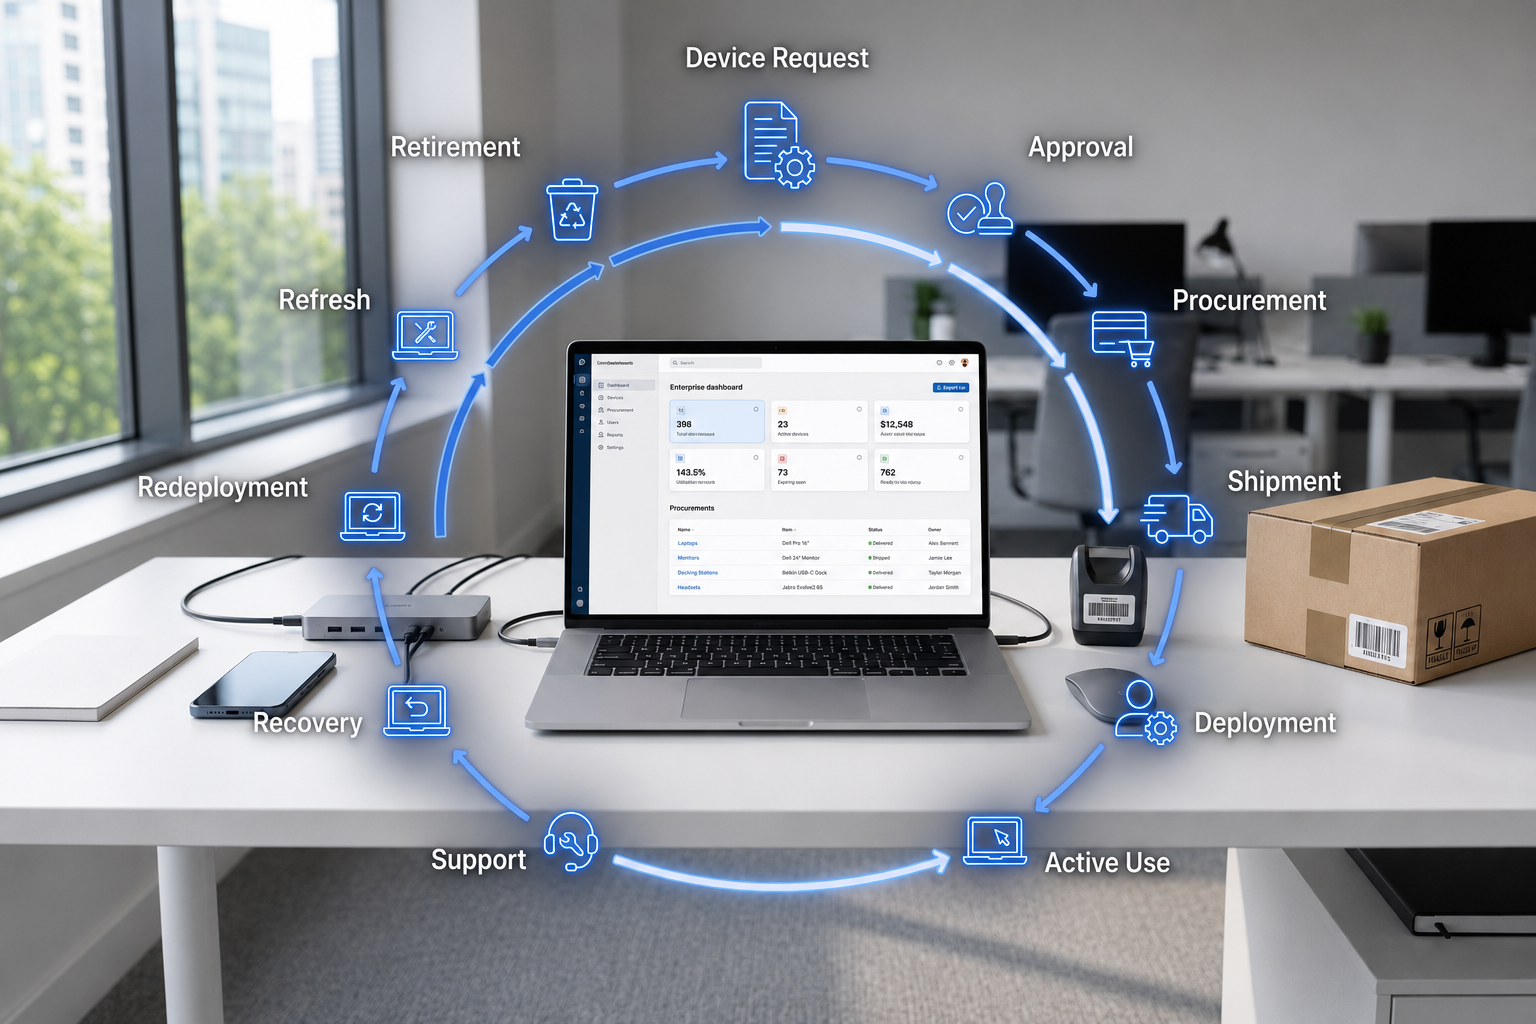
For distributed teams, digital access should also align with the physical device lifecycle. Esevel supports onboarding, offboarding, device management, and IT support, while identity platforms manage user accounts and application access.
FAQs
What is user management?
User management is the process of creating, managing, securing, and removing user accounts and access. It covers authentication, permissions, provisioning, role changes, and offboarding across company systems.
Why is user management important?
User management helps organizations give employees the right access while reducing unnecessary permissions. It also supports security, efficient onboarding and offboarding, and more consistent access control.
What is the difference between user management and access management?
User management covers the full lifecycle of user identities and accounts. Access management focuses specifically on controlling which systems, applications, and data each user is allowed to access.
What are common user management methods?
Common methods include role-based access control (RBAC), attribute-based access control (ABAC), automated provisioning and deprovisioning, single sign-on, multi-factor authentication, and adaptive authentication.
How can companies improve user management for remote teams?
Companies can centralize identity management, automate provisioning and deprovisioning, apply least-privilege access, use strong authentication, and connect access changes with employee onboarding, role changes, and offboarding.
Nguyen Le Nguyen Le is a former Esevel writer / Marketing Consultant who helped build the company’s blog from its early days. From September 2023 to November 2025, she contributed articles that made workplace IT topics clearer and more useful for business readers.
Updated by: Maytiska Omar